Key Takeaways
- Follow a practical XDR implementation roadmap to unify detection, automate response, improve SOC workflows, and measure security outcomes.
- Understand baseline performance before implementation: Measure current detection, investigation, containment, analyst effort, and coverage so improvement can be proven.
- Design the architecture around data quality: Validate timestamps, identity context, asset attribution, retention, ingestion latency, and data completeness.
- Deploy XDR in controlled waves: Establish the platform foundation first, connect network and endpoint telemetry next, then expand into identity, cloud, SaaS, OT, and IoT.
- Automate response according to operational risk: Begin with enrichment and evidence collection before introducing high-impact containment actions.
- Operationalize XDR inside the SOC: Redesign workflows, assign clear ownership, and train analysts by role, so the platform changes how investigations are performed.
- Measure implementation success through outcomes: Track coverage, detection accuracy, investigation speed, containment time, evidence quality, and business value.
Attackers do not respect the boundaries between your endpoint platform, network controls, identity infrastructure, cloud environment, and SIEM. They now use those boundaries.
That gap is one reason enterprises are investing in Extended Detection and Response. But purchasing an XDR platform does not automatically close it.
A successful XDR implementation requires more than connecting telemetry sources and enabling default detections. It requires a deliberate operating model that brings architecture, detection engineering, investigation, response, and measurement together.
This roadmap explains how to move from initial planning to an operational XDR program that delivers measurable outcomes, with a particular focus on how Fidelis Elevate® supports that transition.
What is XDR Implementation?
XDR implementation is the process of integrating network, endpoint, identity, cloud, application, threat intelligence, and other security telemetry into a coordinated detection, investigation, and response architecture.
The XDR implementation process usually include:
- Defining security outcomes and priority use cases
- Assessing existing tools and visibility gaps
- Designing the target data and integration architecture
- Deploying sensors, agents, collectors, and integrations
- Normalizing and correlating security telemetry
- Engineering and validating detections
- Automating approved response actions
- Embedding XDR into SOC workflows
- Measuring detection, investigation, and response performance
- Continuously tuning and expanding the platform
The objective is not simply to put more data into another console. It is to create an operating layer that can follow an attack across security domains, preserve the evidence analysts need, and coordinate response before the adversary completes the next stage of the intrusion.
Why XDR Implementations Underperform
Most unsuccessful XDR projects fail because the organization treats implementation as a technology rollout rather than a security operations transformation.
Common warning signs include:
- Data Without a Use Case: Telemetry is connected before teams define what threats or attack paths they need to detect.
- Coverage That Hides Blind Spots: Endpoint coverage looks strong on paper, while unmanaged and high-risk assets remain invisible.
- Perimeter-Only Network Visibility: Traffic is monitored at the edge, leaving east-west movement and internal attack activity unobserved.
- Identity Context Stays Isolated: Identity and Active Directory activity are not correlated with endpoint and network evidence.
- Security Tools Lack Clear Roles: SIEM, SOAR, EDR, NDR, and threat intelligence tools overlap without defined responsibilities or data flows.
- Default Rules Replace Detection Engineering: Out-of-the-box correlation rules are enabled without tuning them to the organization’s environment, assets, and threats.
- Automation is Introduced Too Early: Response actions are automated without business impact analysis, approval controls, or rollback procedures.
- Investigations Remain Fragmented: Analysts continue moving between disconnected tools instead of investigating through a unified XDR workflow.
- Success Is Measured by Activity: Teams track alerts, events, and integrations instead of improvements in detection, investigation, and containment.
Wrong XDR implementation results in technically integrated security that remains operationally fragmented.
That outcome is especially dangerous now. Verizon’s 2026 DBIR[1] found that vulnerability exploitation had become the leading breach entry point, accounting for 31% of breaches. The same research found third-party involvement in 48% of breaches.
- Early Threat Discovery
- Automating Incident Response Playbooks
- Automating Cyber Terrain Mapping

The Enterprise XDR Implementation Roadmap
An effective roadmap should deliver value incrementally. Trying to connect every source, migrate every control, and automate every response in one release usually creates a long implementation cycle with no clear production milestone.
A more defensible approach is to move through seven controlled phases.

Each phase should have a technical owner, an operational owner, defined dependencies, and measurable completion criteria.
Phase 1: Strategy & Baselining:
The first decision is which security outcomes matter enough to justify the implementation.
For a CISO, the objective might be reducing breach exposure across hybrid infrastructure. For a SOC leader, it could be shortening investigation time and decreasing analyst handoffs. For detection engineering, the priority may be improving coverage for credential access and lateral movement. For a CTO, it may be consolidating redundant infrastructure without weakening control coverage.
Translate those objectives into testable use cases.
Start With Attack Scenarios, Not Product Modules
Examples of implementation-level use cases include:
- Detecting credential misuse followed by suspicious endpoint or network activity
- Identifying lateral movement across managed and unmanaged assets
- Correlating endpoint process execution with command-and-control communications
- Detecting reconnaissance and credential harvesting through deception triggers
- Reconstructing data exfiltration across cloud, endpoint, email, and network channels
- Containing a compromised endpoint while blocking associated network activity
- Investigating activity that occurred before an indicator was classified as malicious
- Prioritizing incidents based on asset criticality, attack progression, and exposure
Each use case should specify:
- The attack behavior being addressed
- The systems and assets involved
- The telemetry required
- The expected detection logic
- The evidence an analyst needs
- The response actions available
- The metric that will demonstrate improvement
This prevents a familiar failure mode: connecting large volumes of telemetry that do not materially improve detection or investigation.
Establish the Baseline
You cannot demonstrate value without knowing the pre-XDR state.
Record current performance for:
- Mean time to detect
- Mean time to acknowledge
- Mean time to investigate
- Mean time to contain
- Alerts reviewed per incident
- Number of console pivots per investigation
- Percentage of priority assets covered
- Percentage of incidents with adequate forensic evidence
- False-positive or non-actionable alert rate
- Percentage of incidents detected internally
- Number of manual actions required for containment
- Analyst hours spent on repetitive enrichment and triage
Avoid optimistic baselines based only on closed tickets. Review a representative sample of investigations and measure the actual analyst workflow.
Phase 2: Architecture and Integration Design
The architecture phase determines whether the platform will become a unified investigation layer or another isolated security system.
1. Map the Existing Security Stack
Document the current environment across:
- EDR and endpoint prevention
- Network detection and response
- Firewalls, proxies, DNS and secure web gateways
- SIEM and log management
- SOAR and case management
- Identity providers and Active Directory
- Email security
- Cloud platforms and SaaS applications
- Vulnerability and exposure management
- Threat intelligence
- Data loss prevention
- OT, IoT and specialized network environments
For each control, capture its data format, API availability, event volume, retention period, asset coverage, owner, and operational purpose.
Then decide whether the XDR platform will:
- Ingest its data
- Enrich its alerts
- Trigger an action through it
- Replace part of its functionality
- Continue operating independently
- Be retired after migration
This is one of the most important XDR implementation best practices. “Integration” should not become a default answer for every existing product. Some tools should remain and some consolidated. Others may provide little value once duplicate detection and investigation capabilities are removed.
2. Design Around Data Quality
Missing identity context, unstable timestamps, or duplicate events can weaken correlation regardless of how advanced the analytics appear.
CISA’s event logging guidance[2] emphasizes establishing a logging baseline that supports threat detection while accounting for operational and resource constraints.
The same principle applies to XDR. Collect the telemetry required to answer a security question. Do not confuse indiscriminate ingestion with visibility.
For every proposed telemetry source, validate:
- Timestamp accuracy and time synchronization
- Asset and identity attribution
- Schema consistency
- Event completeness
- Ingestion latency
- Duplicate event handling
- Encryption and transport security
- Data residency requirements
- Retention and storage costs
- Failure and retry behavior
3. Plan Sensor and Agent Placement Around Attack Paths
Network sensors should be positioned where they can observe meaningful attacker movement, including:
- Internet ingress and egress
- Data center interconnects
- Internal segmentation boundaries
- High-value application environments
- Remote access infrastructure
- Cloud network boundaries
- Connections between IT and specialized environments
- Traffic associated with sensitive data repositories
The point is not to chase an arbitrary coverage percentage. It is to establish coverage over the assets and communication paths that shape enterprise risk.
Phase 3: Core Platform Deployment
Enterprise XDR should be implemented in bounded production waves rather than across the entire environment at once.
| Deployment wave | Primary focus | What to implement | Validation or operational value |
|---|---|---|---|
| Wave 1: Establish Management and Data Foundation | Build a stable, secure XDR foundation before onboarding broad telemetry. |
| Confirm that the platform can process, retain, and retrieve data within the required performance window. |
| Wave 2: Connect High-Value Network and Endpoint Telemetry | Combine endpoint and network evidence to improve detection and attack reconstruction. | Endpoint telemetry:
| Correlated telemetry helps analysts move from identifying a suspicious process to understanding the infrastructure it contacted, the systems it accessed, and the data it attempted to move. |
| Wave 3: Add Identity, Cloud, and Specialized Sources | Expand visibility after the core data pipeline is stable. |
| Extend detection and investigation across identity, cloud, SaaS, specialized environments, and external access paths. |
Do not move to the next wave simply because an integration shows a green status. Validate that the data can support the intended detections and investigations.
Phase 4: Detection Engineering
Default detections may accelerate initial deployment, but they should not define the mature program.
Detection engineering needs to align platform analytics with the organization’s threat model, infrastructure, assets, and risk profile.
1. Use MITRE ATT&CK as a Coverage Model
MITRE ATT&CK[3] provides a common structure for mapping adversary tactics and techniques across Windows, macOS, Linux, identity providers, SaaS, IaaS, network devices, containers, and other enterprise platforms.
Use ATT&CK to answer:
- Which relevant techniques can we detect?
- Which data sources support each detection?
- Which techniques are covered only by a single control?
- Where can cross-domain correlation increase confidence?
- Which detections have been technically validated?
- Which techniques still lack sufficient telemetry?
- What evidence is preserved when the detection fires?
Coverage should be prioritized by exposure and threat relevance rather than by the percentage of the entire framework represented on a dashboard.
2. Correlate Weak Signals into Strong Conclusions
Individual events often look legitimate:
- A PowerShell process starts.
- A user authenticates to a server.
- A system queries Active Directory.
- An endpoint connects to a new domain.
- A privileged account accesses a cloud resource.
- A large data transfer begins.
The value of XDR lies in its ability to determine whether those actions constitute a coherent attack sequence.
3. Validate Detection Content Through Simulation
Every priority detection should be tested using:
- Adversary emulation
- Purple-team exercises
- Controlled attack simulations
- Historical incident replay
- Benign look-alike activity
- Peak data-volume conditions
- Sensor or integration failure scenarios
Validation should confirm more than whether an alert appeared. It should verify:
- The attack stage was classified correctly.
- The relevant asset and identity were attributed.
- Supporting evidence was retained.
- The investigation path was understandable.
- The detection did not depend on unavailable telemetry.
- The response action worked as designed.
- The activity could be reconstructed after the test.
Phase 5: Response Orchestration
Response automation is often where XDR business cases become most aggressive and implementation programs become least disciplined.
Not every response action should be fully autonomous.
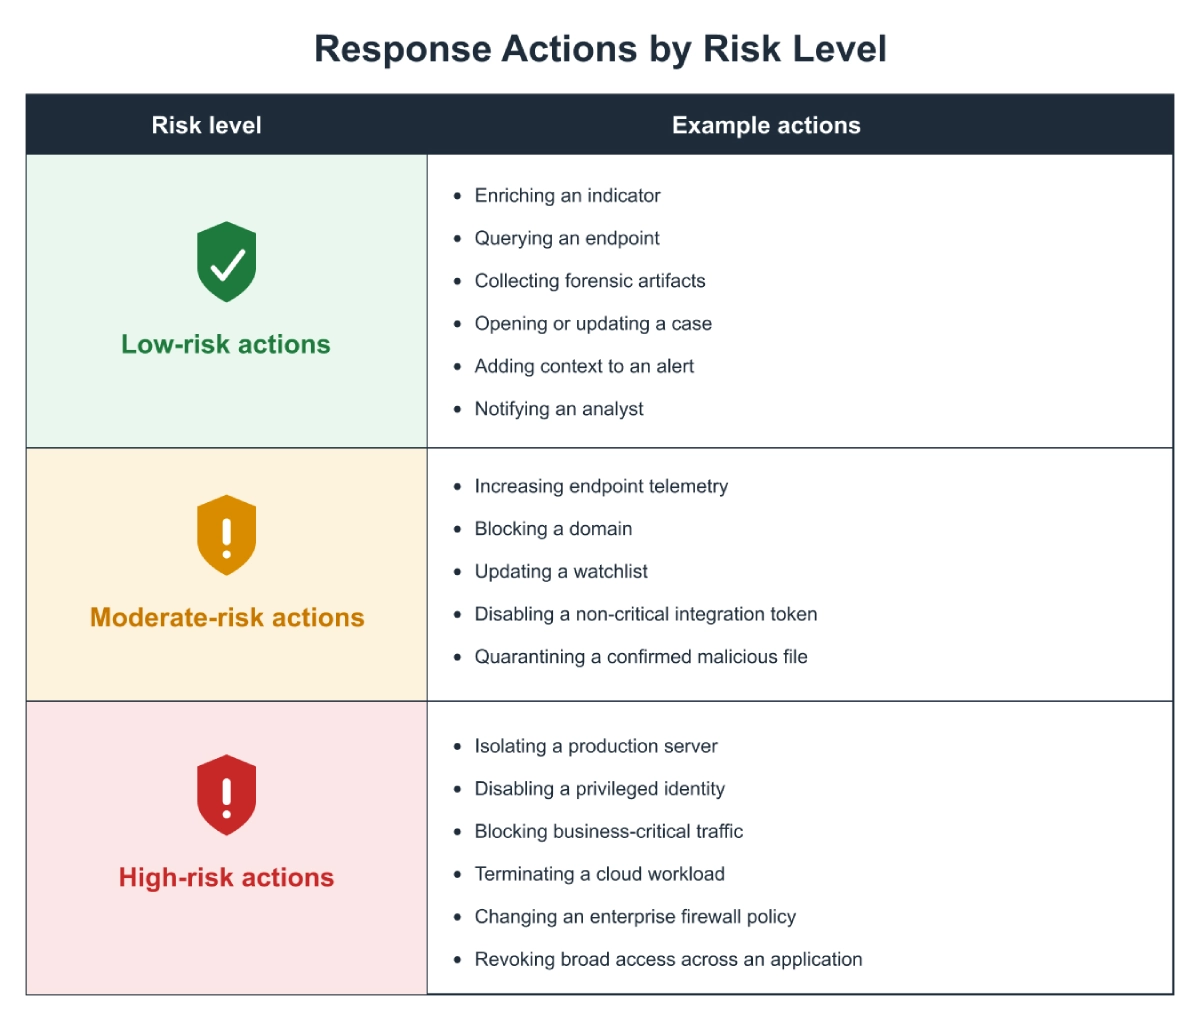
1. Classify Actions by Operational Risk
High-impact actions generally need explicit approval until the organization has validated detection confidence, ownership, dependencies, and rollback procedures.
2. Build Playbooks Around the Full Incident Lifecycle
A useful playbook should cover:
- Detection qualification
- Evidence collection
- Asset and identity enrichment
- Scope determination
- Containment
- Escalation
- Eradication
- Recovery
- Validation
- Documentation and lessons learned
It should also define what happens when an integration fails or an automated action produces an unexpected result.
Fidelis Elevate® supports REST APIs, out-of-the-box connectors, custom API integrations, and webhook-based alert forwarding. Fidelis also supports integrations across SIEM, SOAR, EDR, SSE, threat intelligence, and network technologies, allowing organizations to coordinate responses without discarding existing investments.
That open architecture matters during implementation. Most enterprises are not building a security stack from scratch.
Phase 6: SOC Operationalization
The platform is not operational merely because it is receiving production data. XDR becomes operational when the SOC can use it consistently during triage, investigation, hunting, and response.
1. Redesign the Investigation Workflow
A mature XDR workflow should reduce unnecessary pivots by placing the following in a shared investigation context. The analyst should be able to move through the evidence chain without repeatedly exporting timestamps, hostnames, hashes, and identities between consoles.
2. Define Clear Operational Ownership
Without clear ownership, XDR problems tend to move between security engineering, infrastructure, detection engineering, and SOC operations without resolution.
At minimum, establish ownership for:
- Platform administration
- Integration health
- Data quality
- Detection content
- Threat intelligence
- Response playbooks
- Endpoint deployment
- Network sensor coverage
- Identity and cloud telemetry
- Metrics and executive reporting
- Change control
- Vendor escalation
3. Train by Role
SOC training should be based on how each role uses the platform.
Tier 1 analysts need alert qualification, evidence review, escalation, and approved response procedures.
Tier 2 and Tier 3 analysts need advanced investigation, endpoint and network pivoting, historical search, forensic collection, and scope analysis.
Detection engineers need correlation logic, telemetry dependencies, ATT&CK mapping, test methods, and tuning workflows.
Incident responders and threat hunters need retrospective analysis, session reconstruction, endpoint acquisition, hypothesis-driven querying, and cross-domain timelines.
Platform owners need capacity management, integration monitoring, certificates, retention, backup, updates, and disaster recovery.
Phase 7: Measurement and Optimization
Measuring success of XDR implementations requires a balanced set of metrics. No single KPI proves that the program is working.
| Metric category | Metrics to measure | What the metrics indicate |
|---|---|---|
| 1. Visibility and Data Health |
| Whether the XDR platform has complete, reliable, and timely evidence to support detection and investigation. |
| 2. Detection |
| Whether XDR is producing relevant, validated, and high-confidence detections. The number of enabled rules alone should not be treated as a maturity metric. |
| 3. Investigation |
| Whether XDR is reducing investigation friction and helping analysts reach reliable decisions faster. Measure from the point at which the analyst begins working, not only from ticket creation. |
| 4. Response |
| Whether response actions are fast, consistent, reliable, and safe. The objective is controlled automation, not maximum automation. |
| 5. Business and Program Value |
| Whether the XDR implementation is delivering measurable operational, financial, risk, and governance improvements. |
A Fidelis customer case study provides a useful example of outcome-based measurement. Fidelis reports that a major global bank reduced incident response time from 10 days to five hours after improving its ability to process, index, and investigate relevant traffic. As a vendor-published customer result, it should not be treated as a universal benchmark, but it illustrates the type of before-and-after operational metric an XDR program should track.
Why Fidelis Elevate® Fits an Enterprise XDR Implementation Strategy
Many XDR products begin with one dominant control, usually endpoint security, and extend outward through integrations.
Fidelis Elevate® takes a broader approach.
The platform combines Fidelis Network®, Fidelis Endpoint®, Fidelis Deception®, and Active Directory protection within a unified XDR architecture.
That distinction matters during implementation for several reasons.
Deep Network and Endpoint Evidence
Fidelis Network uses Deep Session Inspection® to reconstruct and analyze network sessions, while Fidelis Endpoint provides process, file, registry, network, and other endpoint activity. Together, they give analysts both host-level and communication-level evidence.
Integrated Deception
Deception is not treated as an isolated honeypot project. Fidelis Elevate® can incorporate decoys, credentials, breadcrumbs, and deception interactions into the broader detection and investigation workflow.
A deception solution trigger can provide a high-confidence signal during reconnaissance, credential misuse, or lateral movement, helping the SOC distinguish malicious exploration from routine administrative activity.
Risk-Aware Cyber Terrain Mapping
Fidelis Elevate® maps assets, data flows, coverage, vulnerabilities, and risk relationships across the environment. The platform’s risk calculation considers factors such as asset importance, coverage, and the severity of observed activity.
That supports a more defensible implementation model. Teams can prioritize sensors, agents, detections, and response workflows according to actual asset risk rather than deploying every capability uniformly.
- Identify and neutralize threats faster
- Gain full visibility across your attack surface
- Automate security operations for efficiency
Cross-Domain Correlation and ATT&CK Mapping
Fidelis Active Threat Detection correlates signals across network, endpoint, deception, sandbox, and third-party sources. It preserves relevant evidence and maps attacker behavior to MITRE ATT&CK, giving analysts a clearer view of attack progression.
Open Integration with Existing Security Investments
Fidelis Elevate® supports connectors and APIs for SIEM, SOAR, EDR, SSE, threat intelligence, and network technologies. That allows enterprises to implement XDR without forcing an immediate replacement of every established control.
This is where Fidelis XDR implementation can be particularly valuable for mature SOCs. It provides a path to unify detection and investigation while retaining tools that still serve a clear operational or compliance purpose.
Citations: